Topic
Risk & Security
Cybersecurity Awareness Month: Securing the Next 250 with Cyber Threat Hunting
This Cybersecurity Awareness Month, learn from Tanium why cyber threat hunting is the next requirement for security teams to combat modern cyber threats.
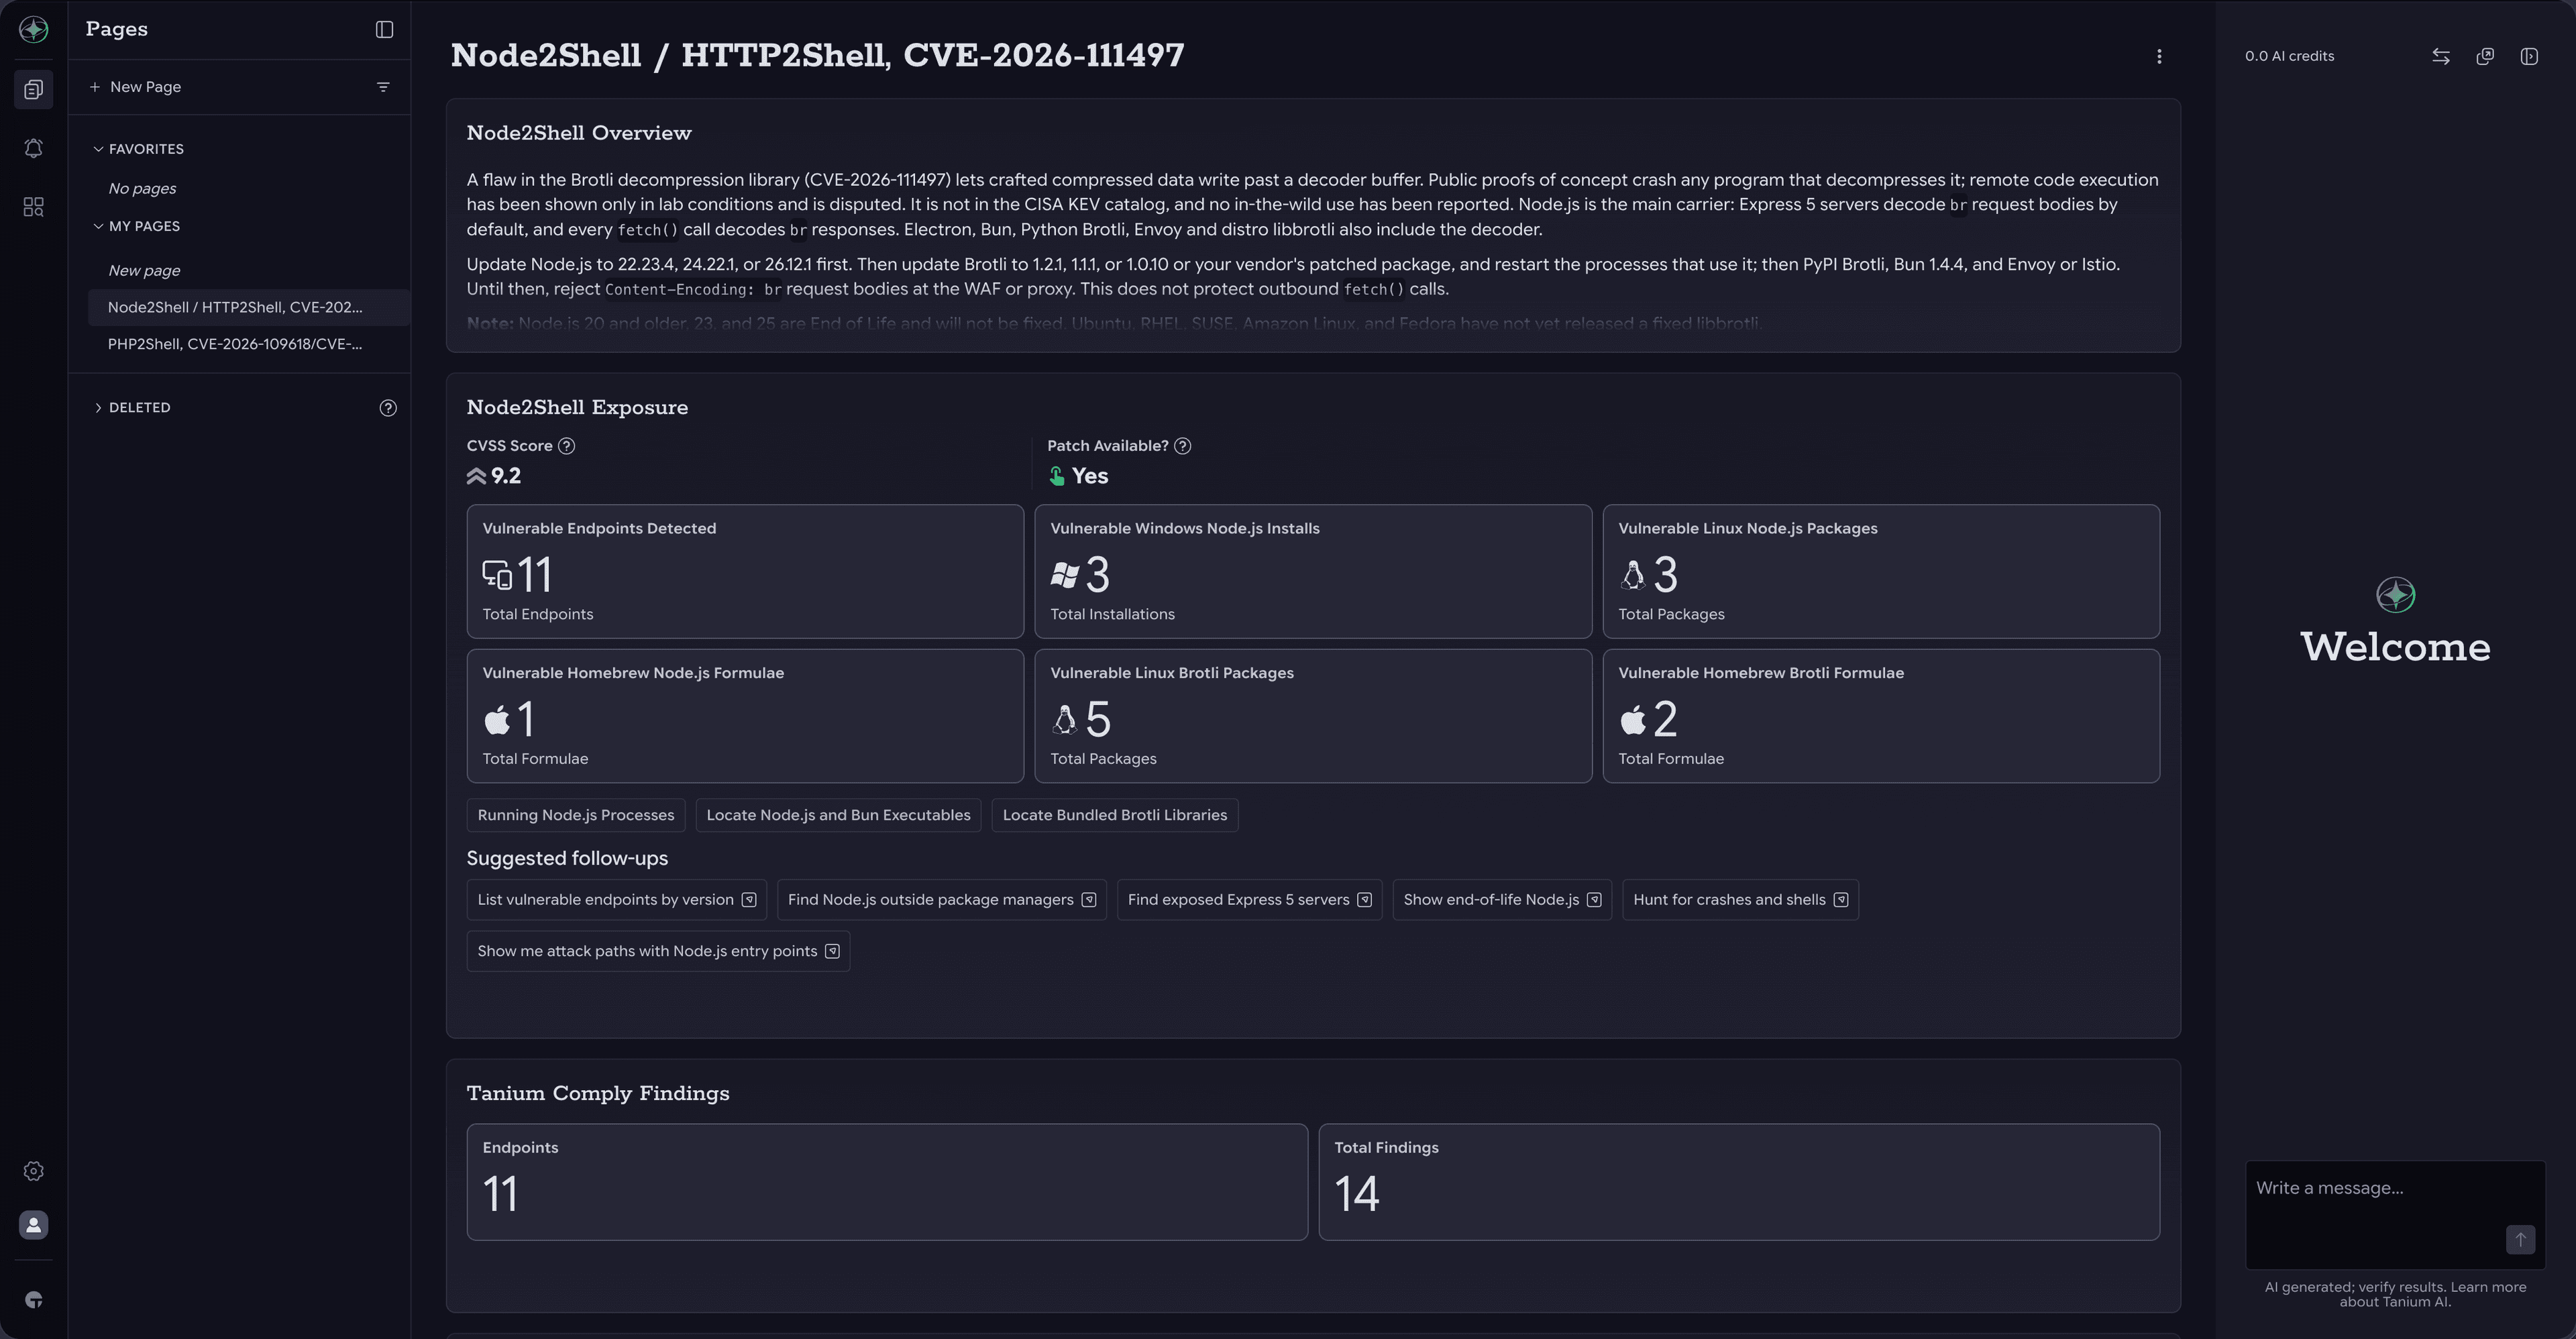
HTTP2Shell: Find and Fix Vulnerable Brotli Copies with Tanium
A critical flaw in Google's Brotli decoder (CVSS 9.2) can let a remote attacker crash or take over apps that decompress Brotli data. Update Node.js, Python Brotli and Bun now.
eMudhra CA Compromise: Find and Fix Your Exposure with Tanium
Private keys for eight eMudhra intermediate CAs can be calculated from their public certificates. Browsers block them once updated; most other software needs a trust store update.
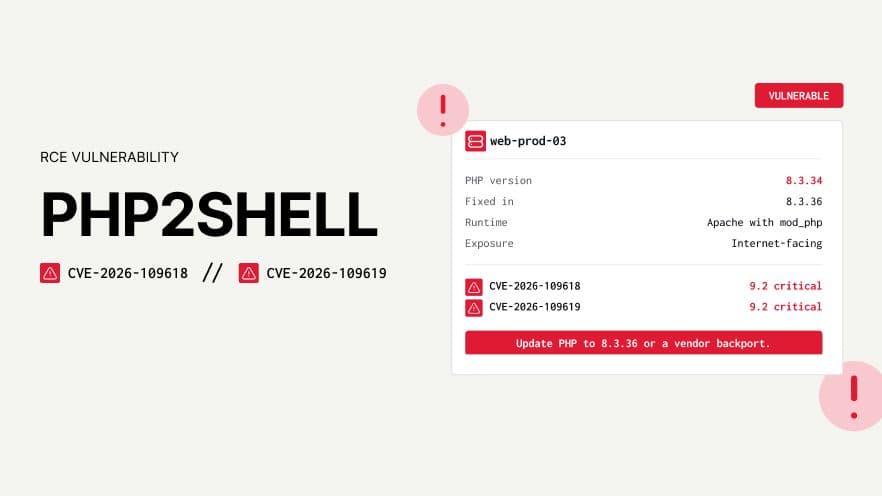
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619
Two critical flaws in PHP core (CVSS 9.2) let an unauthenticated attacker run code with a crafted web request. Patch to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
Critical Netlogon RCE on domain controllers (CVE-2026-41089)
A critical, unauthenticated remote code execution vulnerability in Windows Netlogon (CVE-2026-41089, CVSS 9.8) lets a remote attacker run code as SYSTEM on a domain controller. Patch all domain controllers in the same maintenance window with the May 2026 security updates.
World Cup ’26: What it takes to secure the world's biggest sporting event
For cyber defenders, the work is invisible by design. For fans, a little awareness goes a long way.
Tanium at the Gartner Security & Risk Management Summit 2026
As security leaders prepare to tackle the industry’s most urgent priorities, Tanium will bring the real-time intelligence and agentic AI capabilities needed to close the gap between insight and execution.
May 2026 GitHub breach: Extension hygiene is still a challenge–so what can we do about it?
On May 20, 2026, GitHub disclosed that an employee device was compromised through a malicious VS Code extension, with attackers claiming to have exfiltrated roughly 3,800 internal repositories.
Mini Shai-Hulud supply chain attack: Why this campaign changes how defenders should think about trusted software
The Mini Shai-Hulud supply chain attack compromised more than 170 packages across npm and PyPI, including packages from TanStack, Mistral AI, and Guardrails AI, by hijacking legitimate CI/CD publishing workflows to distribute malicious versions that still carried apparently valid provenance signals.
Copy Fail (CVE-2026-31431): What Linux administrators need to know now
Copy Fail, or CVE-2026-31431, is a Linux kernel local privilege escalation vulnerability that can let an unprivileged local user corrupt page-cache-backed file data under specific conditions and potentially escalate privileges. Exposure depends on the running vendor kernel and backported fixes. Installing a vendor-provided kernel fix is the primary remediation, with temporary mitigations available in some environments if patching is delayed.
Vercel security incident: What the breach reveals about OAuth trust, supply chain risk, and response speed
Public reporting suggests the incident involved abuse of a third-party application that had been granted OAuth access to a Vercel employee account, enabling unauthorized access to some internal resources. Certain customer‑related tokens, environment variables, or other access artifacts may have been exposed, though Vercel has not stated that password theft was part of the initial access path. The breach illustrates how trusted SaaS integrations and delegated access have become a significant attack surface for enterprises with interconnected developer workflows, even when no software vulnerability in production infrastructure is exploited.
Understanding shadow AI in your endpoint environment
Learn how shadow AI appears on endpoints, from local models to MCP servers, and why visibility, governance, and secure configuration matter now.